
CISA warns of critical vulnerability in MikroTik RouterOS
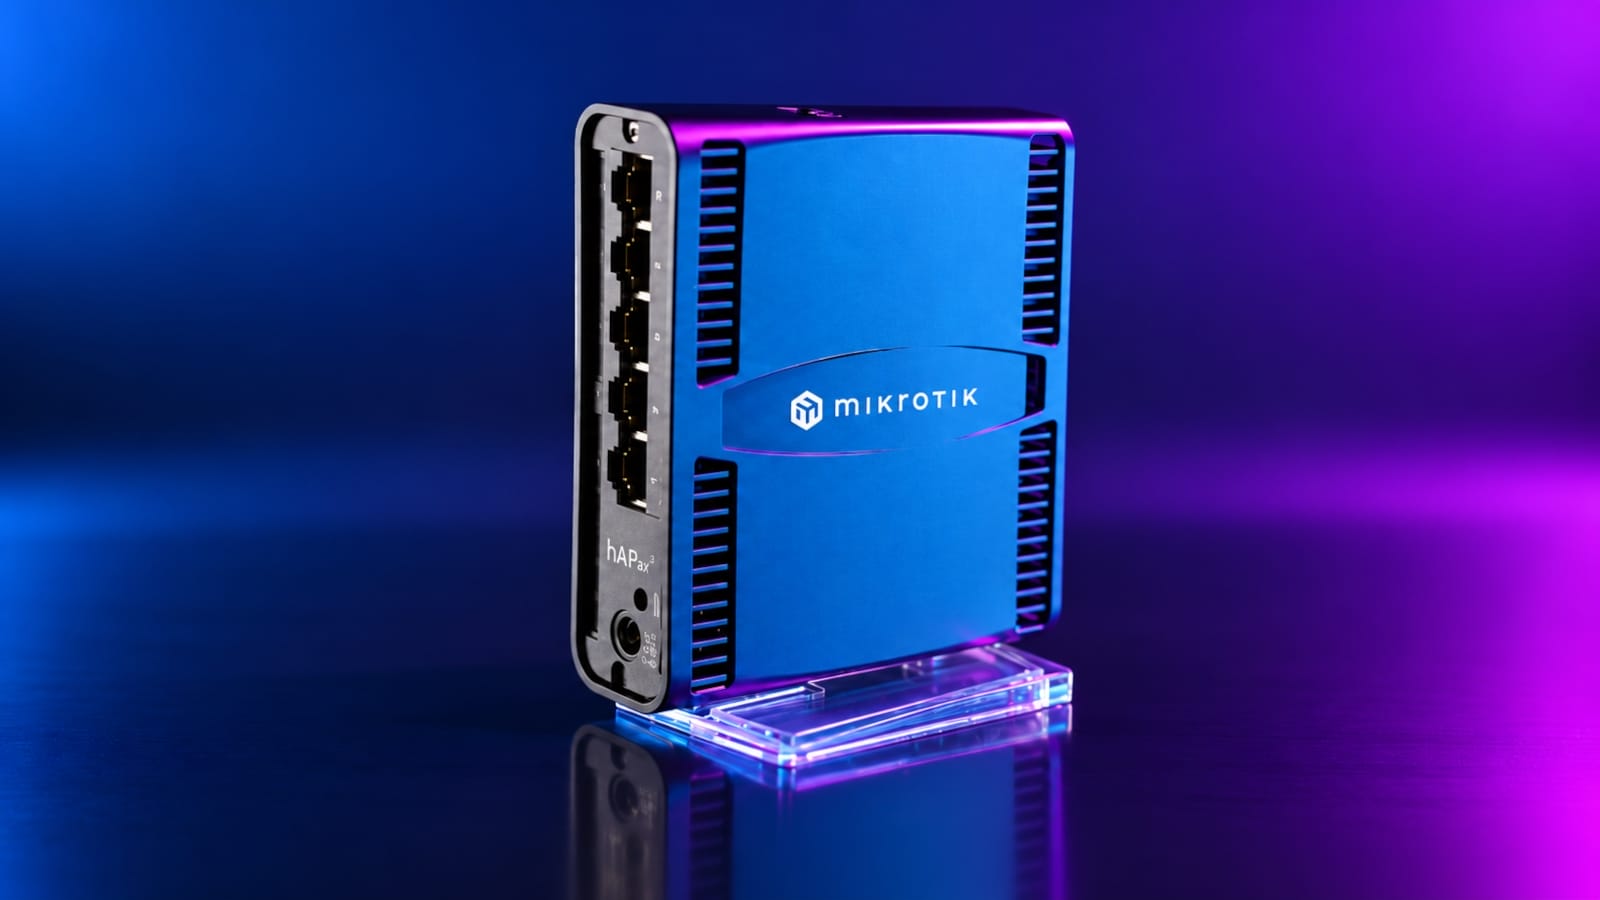
CISA has reported a critical security vulnerability in MikroTik RouterOS that could lead to remote code execution.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning regarding a critical security vulnerability in MikroTik RouterOS. This vulnerability could allow attackers to execute code remotely or cause a denial-of-service condition. The agency has emphasized that affected systems should be updated immediately to prevent potential attacks.
The vulnerability affects a specific function in MikroTik RouterOS that allows attackers to access the system without authentication. This means that an attacker does not even need a password to take control of the device. CISA has classified the severity of this flaw as critical, indicating that it could be actively exploited.
Details of the Vulnerability
The exact technical designation of the vulnerability has not been published yet; however, CISA has pointed out that it exists in several versions of MikroTik RouterOS. The agency recommends that all administrators of MikroTik devices promptly update their systems to the latest version to protect against possible attacks. The vulnerability could not only lead to data loss but also jeopardize the entire network infrastructure.
CISA has also noted that attackers may be able to install malware on the affected devices, potentially leading to further compromise of the network. This type of attack could not only threaten the integrity of the data but also the confidentiality of information transmitted over the network.
In addition to the recommendations for updating, CISA has also advised reviewing network security and implementing additional security measures if necessary. This includes monitoring network traffic for suspicious activities as well as implementing firewalls and Intrusion Detection Systems (IDS) to prevent unauthorized access.
Reactions from the Security Community
The security community has taken CISA's warning seriously and urges all affected users to act quickly. Experts emphasize that a rapid response to such security vulnerabilities is crucial to minimize the impact on network security. Many companies using MikroTik RouterOS have already begun implementing security updates to protect their systems.
CISA has also stressed that the vulnerability poses a risk not only to businesses but also to private users of MikroTik devices. As many of these devices are used in households and small offices, a successful attack could have far-reaching consequences. The agency has therefore urged all users to inform themselves about the risks and take appropriate measures.
The discovery of this vulnerability comes at a time when cyberattacks on network infrastructures are increasing worldwide. CISA has previously warned about similar vulnerabilities and emphasized that network security is a shared responsibility. Collaboration between authorities, businesses, and users is essential to ensure safety in the digital space.
CISA will continue to provide information on this vulnerability and keep the public informed about possible developments. Users of MikroTik RouterOS should regularly check the official channels of CISA and MikroTik to stay updated.
Ähnliche Artikel
New Security Threats from AI Models
Current reports indicate that AI models are opening new attack vectors that are often overlooked. Vulnerabilities in mod...
TeamViewer warns of critical security vulnerabilities
TeamViewer urges users to immediately perform security updates to address serious weaknesses....
Microsoft improves Entra ID protection starting October 2026
Microsoft announces that the Entra ID authentication service will be better protected against script injection attacks s...
Zammad Zero-Day Vulnerabilities Enable AI-Driven Network Attack
DIVD reports on a network attack that was made possible by two zero-day vulnerabilities in the Zammad ticketing system....

comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen