
Microsoft Teams as a Target for Cyber Attacks
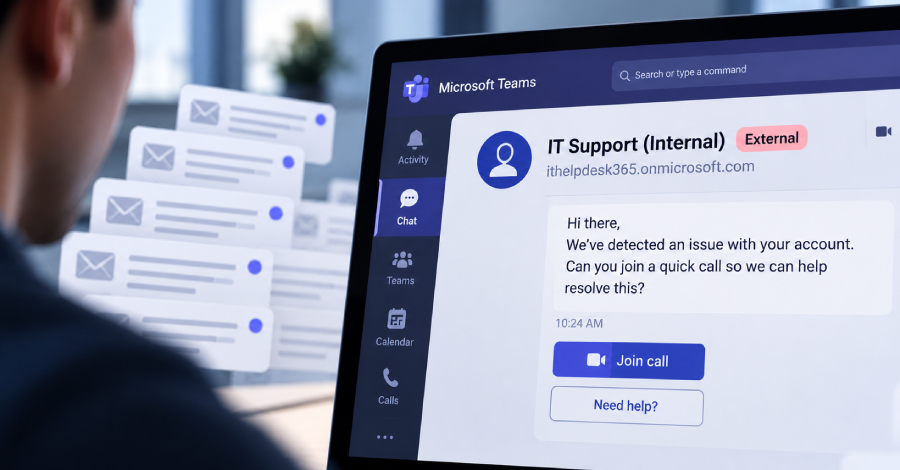
Cybercriminals are using Microsoft Teams for fraud attempts and malware distribution. Experts warn of a recurring pattern.
Cybersecurity researchers have released alarming reports about a new wave of cyberattacks utilizing Microsoft Teams as a platform. These attacks are based on a recurring method of social manipulation that has been observed in hundreds of cases. The perpetrators use the external chat creation feature in Microsoft Teams to impersonate IT support and spread malware or ransomware.
The attackers often use temporary accounts referred to as "Throwaway Tenants" to obscure their identity. These accounts allow them to act quickly and retreat after the attack without leaving traces. Researchers have found that this tactic is identical in many cases, indicating an organized approach by the cybercriminals.
Growing Threat of Social Engineering
The attacks are not limited to a specific region but affect companies worldwide. The perpetrators often target employees in various departments to gain trust and obtain sensitive information. The use of Microsoft Teams as a communication tool makes it easier for attackers to reach their victims, as many companies already use this platform for internal communication.
Another concerning element of these attacks is the fact that they are often very well thought out. The attackers create fake profiles that resemble real IT staff and use technical jargon to enhance their credibility. This makes it difficult for victims to identify the fraudsters and respond in time.
Researchers warn that the attacks aim not only to spread malware but also to steal corporate data or extort ransom. In many cases, companies have suffered significant financial losses after falling victim to these fraud attempts. The attackers exploit the fear and uncertainty of employees to achieve their goals.
Prevention Measures and Security Awareness
To protect against this type of attack, it is crucial for companies to educate their employees about the risks of social engineering. Training on recognizing phishing attempts and other fraudulent activities should be conducted regularly. Additionally, companies should establish clear guidelines for handling external communication requests.
Implementing additional security measures, such as multi-factor authentication, can also help minimize the risk of a successful attack. Companies should also regularly review their IT infrastructure to identify and address vulnerabilities. Collaborating with cybersecurity experts can help improve security posture and detect potential threats early.
The threat of cybercrime is constantly evolving, and companies must act proactively to protect themselves. The use of Microsoft Teams as a target for attacks shows that even widely used and trusted platforms are not immune to abuse. Researchers emphasize that raising awareness of these threats and implementing appropriate security measures is of utmost importance.
Current statistics show that the number of cyberattacks utilizing Microsoft Teams as a platform has significantly increased in recent years. Companies are challenged to face these challenges and adjust their security strategies accordingly.
Ähnliche Artikel

Volt Typhoon and the Silent Train Network
The cyber espionage group Volt Typhoon has used a secret network called Silent Train for cyber attacks....

CISA warns of exploitation of critical Node2Shell vulnerability
CISA has confirmed that hackers are exploiting a critical vulnerability called Node2Shell. The threat affects multiple s...

Municipalities demand better protection against cyber attacks
The Association of Cities and Municipalities calls for more measures against cyber attacks, especially after the PHP sec...

PHP2Shell Attack Compromises U.S. Government Network
An AI-assisted cyber attack has infiltrated 25 servers and jeopardized a network with connections to the U.S. government...

comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen