
Zero-Day Security Vulnerability Discovered in MONAI Label
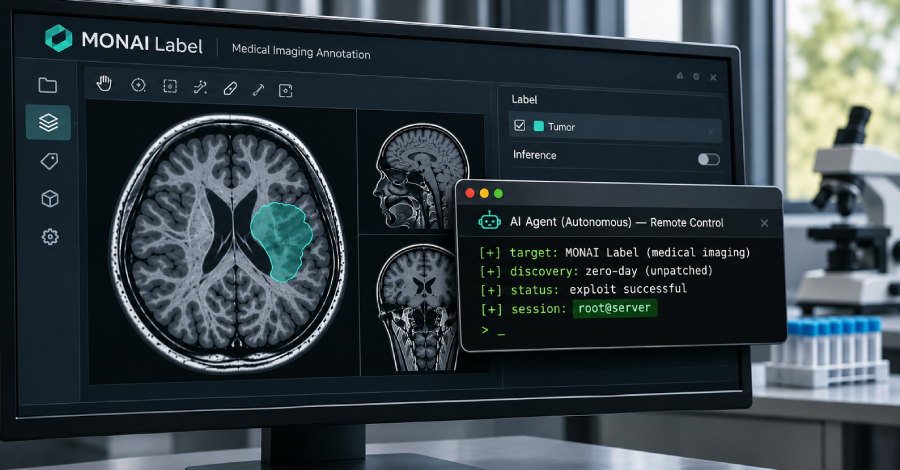
Hackers with AI agents find critical vulnerability in medical software.
In an alarming development, hackers allegedly linked to China have deployed autonomous AI agents to discover a previously unknown security vulnerability in the medical imaging software MONAI Label. This vulnerability allows attackers to gain root access to a university server without a user account. Amazon Threat Intelligence reported on the incident and the associated risks this week.
The discovered vulnerability affects versions of MONAI Label 0.8.5 and earlier when operated in the default configuration. The security flaw allows an attacker to write files outside the intended storage folder of the server. This could potentially lead to data loss or the compromise of sensitive information stored on these servers.
MONAI Label is an open-source software widely used in medical imaging by many research institutions and clinics. The software is often used for analyzing image data in radiology and other medical disciplines. The discovery of this security vulnerability raises serious questions about the security and integrity of the data processed in these systems.
Attack Patterns and Impacts
The use of AI agents to identify vulnerabilities is an increasingly common phenomenon in cybercrime. This technology enables attackers to search for security vulnerabilities more efficiently and quickly than would be possible manually. The fact that these attackers were able to find a critical vulnerability in widely used software highlights the dangers associated with the increasing automation in cybercrime.
The impacts of such an attack could be far-reaching. Universities and research institutions using MONAI Label could not only jeopardize their data but also the trust in their systems and the integrity of their research results. The possibility that sensitive patient data could be compromised could also lead to legal and ethical consequences.
The vulnerability has been classified as critical by Amazon Threat Intelligence, meaning immediate action is required to address it. The developers of MONAI Label now face the challenge of identifying the vulnerability and developing a patch to ensure the software's security. Until an official solution is available, users of the software are urged to review their systems and take security precautions as necessary.
Reactions from the Security Community
The discovery of this vulnerability has raised concerns in the security community. Experts warn that such attacks could become more frequent in the future, especially as cybercriminals continue to leverage AI technologies to find security gaps. The discussion about the need for more robust security measures in software development is reignited by this incident.
Some security experts are calling for increased collaboration between software developers and security professionals to identify and address potential vulnerabilities early. Implementing security audits and penetration testing during the development process could help prevent similar incidents in the future.
The MONAI community has already responded to the discovery and is working on a solution. The developers have announced that they will prioritize the security vulnerability and provide a patch as soon as possible. Users are encouraged to update their software to the latest version as soon as it becomes available to protect themselves from potential attacks.
The security vulnerability in MONAI Label is another example of the challenges facing the technology industry, particularly in the field of medical software. The combination of advanced technology and sensitive data requires constant vigilance and innovation to ensure security.
Ähnliche Artikel
Testing Cyber Resilience in Healthcare
A new security framework for assessing cyber resilience in hospitals takes into account software, infrastructure, and hu...
Microsoft Entra Connect Health: Data Leak Discovered
Microsoft warns of a data leak in Entra Connect Health that allowed attackers access to sensitive information....
BADBOX Botnet Returns to Ad Fraud with Record Numbers
The BADBOX botnet has set a new record with 40 billion daily ad requests, marking its return to ad fraud....
Bell Canada confirms data breach due to hacker attack
Bell Canada has confirmed a security incident in which a hacker stole data from business customers....
comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen