
Oracle releases security updates for Java SE
Oracle has released security updates for 11 Java SE vulnerabilities, including a critical RCE flaw in OpenJDK.
Oracle released security updates on November 17, 2026, for a total of 11 vulnerabilities in Java SE. These vulnerabilities can potentially be exploited remotely without authentication. Oracle's security advisory indicates that the vulnerabilities have a maximum CVSS 3.1 severity score of 8.1. This makes them a serious risk for users and businesses that use Java SE in their applications.
Among the published vulnerabilities is a particularly critical Remote Code Execution (RCE) flaw identified as CVE-2026-114938. This vulnerability affects OpenJDK and could allow attackers to execute malicious code on affected systems. The discovery of this flaw has drawn the attention of security experts, as it could have significant implications for the security of Java applications.
Details on the Security Updates
Oracle's security updates aim to address the identified vulnerabilities and enhance the security of the Java SE platform. The 11 vulnerabilities cover various components and affect both the runtime environment and the development environment of Java. Oracle recommends that all users install the updates as soon as possible to protect their systems from potential attacks.
Oracle's security advisory highlights that the vulnerabilities are present not only in the Java SE version but also in OpenJDK. This is particularly concerning, as OpenJDK is a widely used open-source implementation of Java that is employed in many applications and systems. The prevalence of OpenJDK increases the risk that attackers could exploit the vulnerabilities.
The CVSS score of 8.1 indicates that the vulnerabilities are classified as high-risk. This means that the likelihood of a successful attack is high and the potential impact on the affected systems could be significant. Businesses and developers using Java SE or OpenJDK should therefore exercise caution and promptly apply the recommended security updates.
Reactions from the Security Community
The security community has taken note of the discovery of the critical RCE flaw in OpenJDK with concern. Experts warn that attackers may already be actively attempting to exploit the vulnerability before most users have installed the updates. This could lead to an increase in cyberattacks targeting Java-based applications.
Some security experts recommend that companies review their security policies and ensure that all systems using Java SE or OpenJDK are up to date. Implementing additional security measures, such as intrusion detection systems and regular security audits, could also help minimize the risk of attacks.
The release of Oracle's security updates is an important step toward improving the security of Java applications. However, users and businesses are urged to take proactive measures and ensure that they apply the latest security updates to protect their systems. The threat of cyberattacks remains a serious issue, and software security is of utmost importance.
Ähnliche Artikel
CISA warns of critical Java security vulnerability
CISA urges immediate remediation of a critical security vulnerability in Oracle Java that can lead to remote code execut...

N-able releases critical security update for N-central
N-able has released an important update for N-central that fixes 17 security vulnerabilities and protects the platform....
Security vulnerabilities in Danfoss refrigeration control systems
Six unprotected vulnerabilities in Danfoss AK-SM800A could allow attackers to gain access....
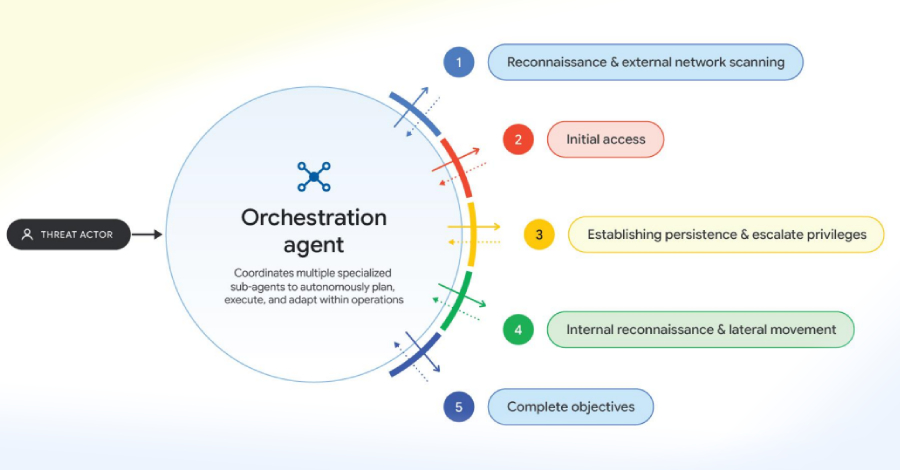
AI-assisted cyberattacks are on the rise
Google warns against the use of AI by hackers to carry out complex cyberattacks....
comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen