
Security vulnerability discovered in Barracuda Email Gateway
Two critical security vulnerabilities in the Barracuda Email Security Gateway allow root access without login. Patches have been released.
In an alarming security report, experts have identified two critical vulnerabilities in the Barracuda Email Security Gateway that allow attackers to gain root access to the system without needing to log in. These vulnerabilities, classified as CVE-2026-116606 and another unnamed gap, can be exploited in a chain reaction to gain complete control over the device. Barracuda Networks released patches on Monday to address these security risks.
The first vulnerability, CVE-2026-116606, is an authorization bypass that allows an unauthenticated attacker to restore certain functions of the system. This means that an attacker exploiting this vulnerability can access critical system functions without needing to log in first. The ability to execute root commands poses a significant risk to the integrity and confidentiality of the data processed through the Barracuda system.
The second vulnerability, detailed in the security report by the company watchTowr, complements the first and allows attackers to further exploit the privileges gained through the authorization bypass. This chain reaction of vulnerabilities is particularly concerning as it enables attackers to penetrate deep into the system and potentially compromise other connected systems as well. The combination of these two vulnerabilities could lead to a comprehensive security incident.
Response from Barracuda Networks
Following the discovery of these vulnerabilities, Barracuda Networks responded promptly and released security updates aimed at closing the identified gaps. The patches were made available on Monday and should be installed immediately by all users of the Barracuda Email Security Gateway. The company has also recommended regularly checking systems for updates to ensure that all security measures are up to date.
The security firm watchTowr emphasized in its report that the discovery of these vulnerabilities highlights the need for companies to regularly review and update their security protocols. The possibility that attackers can gain root access without authentication is a serious risk that should not be ignored. Companies using Barracuda products are urged to implement the new patches immediately to protect their systems.
Impact on Businesses
The impact of these security vulnerabilities could be significant for businesses relying on the Barracuda Email Security Gateway. A successful attack could not only lead to data loss but also to a loss of trust among customers and partners. The possibility of sensitive information being compromised could have far-reaching legal and financial consequences.
IT security experts advise reviewing and adjusting security policies as necessary to ensure that all employees are informed about the risks and know how to recognize potential attacks. Training employees on cybersecurity is a crucial step in minimizing the risk of security incidents. Companies should also consider implementing additional security measures to further secure their systems.
The discovery of these vulnerabilities underscores the ongoing threat of cyber attacks and the necessity for companies to take proactive measures to protect their systems. The security landscape is constantly evolving, and businesses must remain vigilant to address changing threats. Barracuda Networks patched the vulnerabilities in its Email Security Gateway on November 7, 2026.
Ähnliche Artikel
Russia recruits teenagers for attacks?
Indications suggest that Russia is recruiting young people online for violent actions. Arson attacks and knife assaults ...
Cyberattacks on Supermarkets: Security Authorities Active
Following cyberattacks on refrigeration systems in supermarkets, security authorities are getting involved. The Interior...
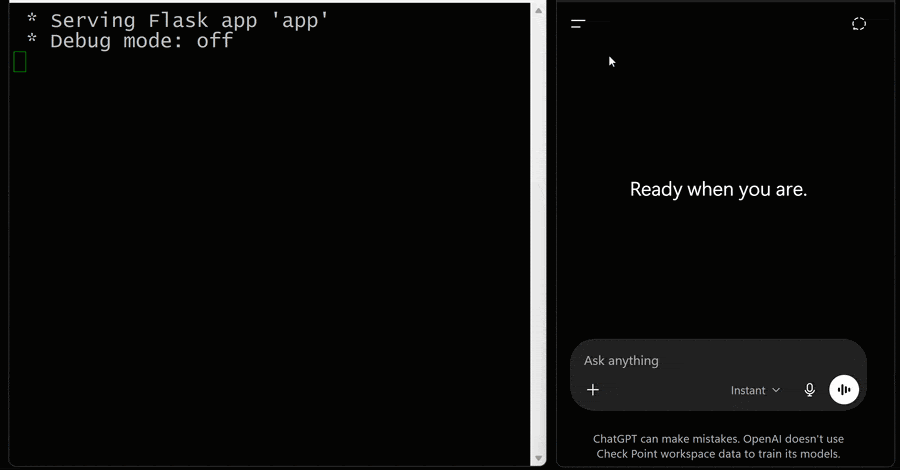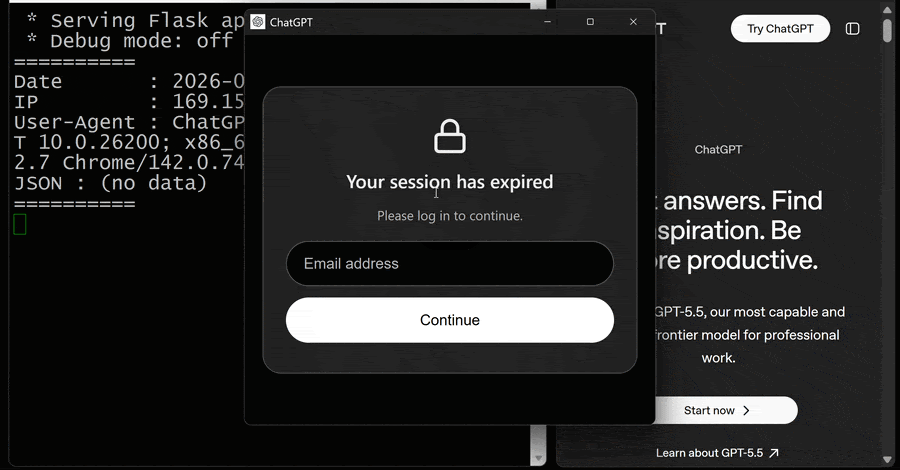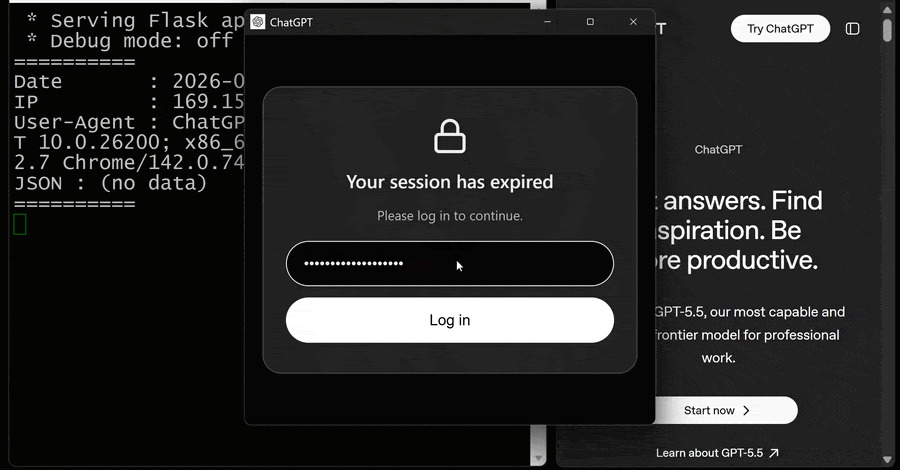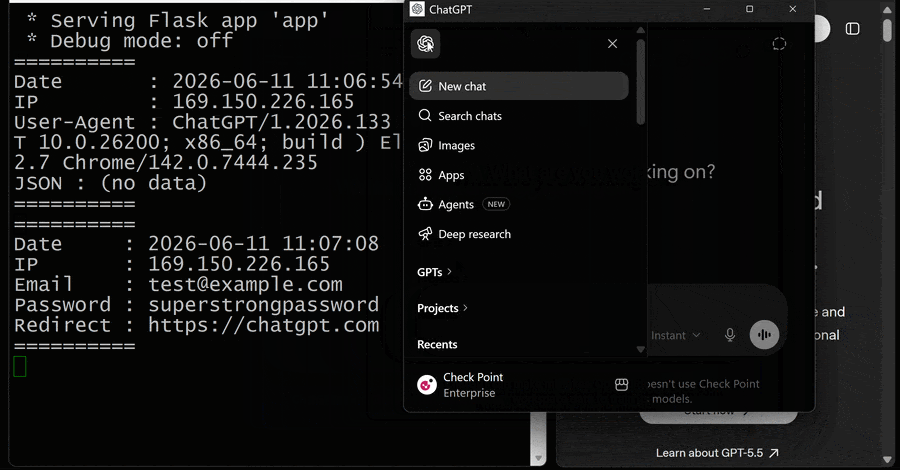
Security vulnerability discovered in ChatGPT's lockdown mode
Researchers have uncovered a security vulnerability in OpenAI ChatGPT's lockdown mode, which has now been fixed....
FBI and CISA warn of cyberattacks on cooling systems
US authorities warn of targeted cyberattacks on industrial cooling systems that can lead to food spoilage and hazards....
comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen