
Security vulnerabilities in Danfoss refrigeration control systems
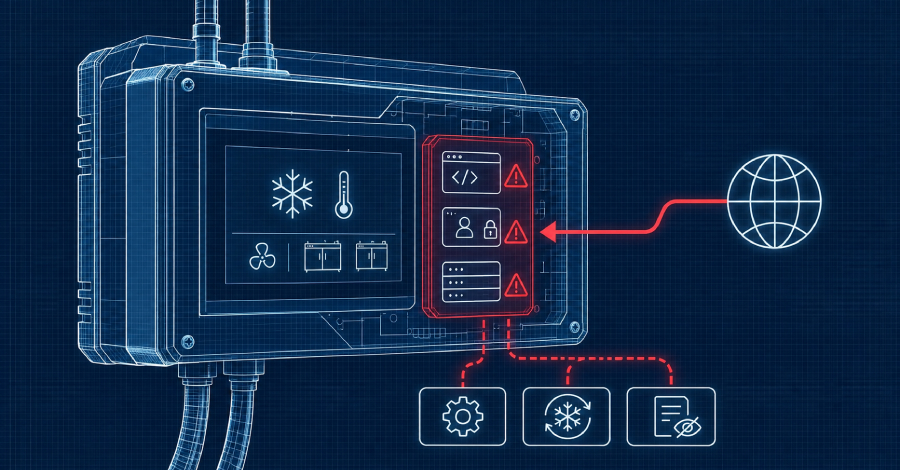
Six unprotected vulnerabilities in Danfoss AK-SM800A could allow attackers to gain access.
Six vulnerabilities in the Danfoss AK-SM800A refrigeration control systems could allow attackers to take control of the devices without needing to log in. This was announced by the Dutch security consultancy Midnight Blue this week. The vulnerabilities are particularly concerning as there is currently no patch available to address the issues. The latest firmware version 5.4.0 does not fix the vulnerabilities.
The affected controls are commonly used in commercial refrigeration systems, significantly increasing the potential impact of an attack. The possibility of unauthorized access could not only lead to data loss but also jeopardize the safety of the entire refrigeration system. The security researchers at Midnight Blue have thoroughly investigated the vulnerabilities and warn of the risks associated with using the affected devices.
Warnings from Government Authorities
Government authorities in Belgium, Ireland, and Germany have urged operators of refrigeration systems to exercise special caution this week. The authorities recommend monitoring the systems and implementing security measures to prevent potential attacks. The warnings come at a time when cyberattacks on critical infrastructures are increasing worldwide.
The security gaps in the Danfoss controls could allow attackers to manipulate the systems, potentially leading to severe disruptions. Affected companies are urged to review their security protocols and implement additional protective measures if necessary. The situation highlights the need to regularly check and apply security updates.
Technical Details of the Vulnerabilities
The vulnerabilities in the Danfoss AK-SM800A controls are classified as critical. They allow attackers to access the systems without authentication. This could lead to a complete takeover of the control, posing significant risks to operational safety. The exact technical workings of the vulnerabilities have been thoroughly documented by Midnight Blue.
The researchers have found that the vulnerabilities exist in various modules of the control, increasing the complexity of remediation. As no patch is available, operators are left with the option of isolating their systems or taking additional security measures to minimize the risk of an attack. The situation requires swift action to prevent potential damage.
The discovery of these vulnerabilities raises questions about the overall security of industrial control systems. Many companies rely on such systems to manage their operations, and the possibility of unauthorized access could have catastrophic consequences. The security situation remains tense as operators await further information and potential solutions.
Ähnliche Artikel

N-able releases critical security update for N-central
N-able has released an important update for N-central that fixes 17 security vulnerabilities and protects the platform....
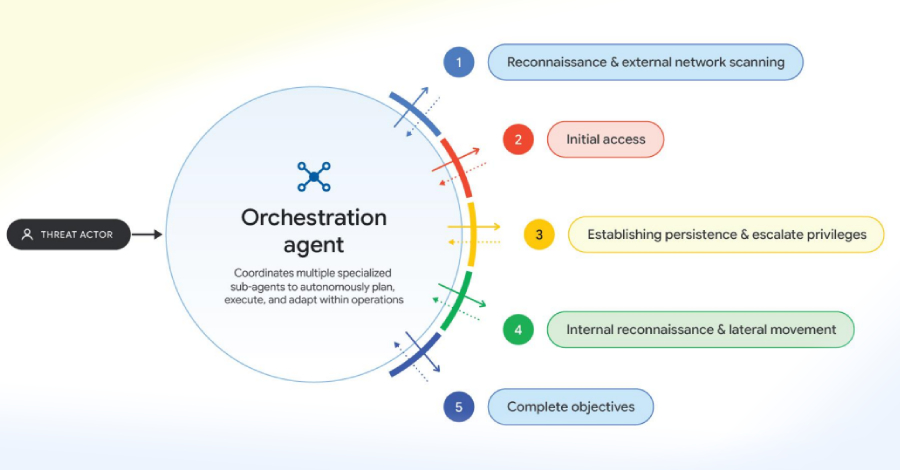
AI-assisted cyberattacks are on the rise
Google warns against the use of AI by hackers to carry out complex cyberattacks....
Java4Shell: Critical Bug Discovered in Java
Oracle releases eleven updates against Remote Code Execution in Java, including the highly risky Java4Shell....
Identity blind spots jeopardize security operations
A webinar highlights how identity blind spots endanger security operations and what measures are necessary to close them...
comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen