
Google warns of LLMjacking attacks
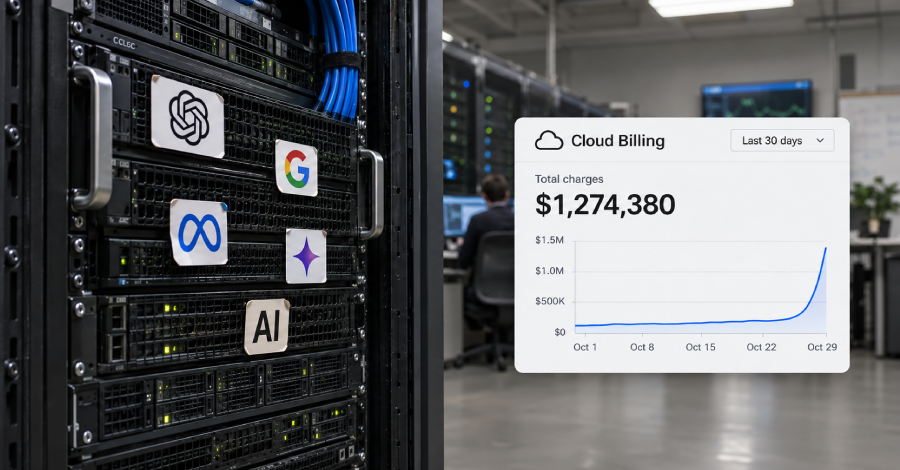
Google warns of LLMjacking, which can cost companies up to 1 million dollars.
Google warned on Monday of a new threat that could significantly burden companies. This threat, known as LLMjacking, refers to attacks where criminals take over access to large language models (LLMs) to exploit costly computing resources and AI services. According to Google, the costs for affected companies can reach up to 1 million dollars.
LLMjacking is a form of resource hijacking specifically designed for the era of large language models. Attackers gain access to API keys through various methods, including phishing, source code leaks, misconfigured environments, or exposed client code. These techniques allow attackers to utilize the computing power and services of companies without their knowledge.
Methods of LLMjacking
Attackers often use phishing attacks to trick employees in companies into revealing their credentials. This method has proven particularly effective, as many employees are not adequately trained to recognize such attacks. Additionally, leaks of source code that occur in public repositories or through insecure practices can also enable attackers to access API keys.
Another risk lies in misconfigured environments, which make it easier for attackers to access sensitive data. If companies do not properly secure their cloud services, they can easily fall victim to LLMjacking. Exposed client code that is not sufficiently protected also poses a significant risk, as it can provide attackers direct access to the resources they need.
The financial impact of LLMjacking can be devastating for companies. Google reports that some companies have already lost up to 1 million dollars in cloud costs due to these attacks. These high costs result from the unauthorized use of computing resources, which are typically expensive, especially when used on a large scale.
Reactions and Preventive Measures
In response to this threat, Google has urged companies to review and improve their security practices. It is recommended to conduct training for employees to raise awareness of phishing attacks and emphasize the importance of securely handling credentials. Additionally, companies should regularly check their cloud environments for security vulnerabilities and ensure that all configurations adhere to best security practices.
Furthermore, companies should ensure that their API keys and other sensitive information are not stored in publicly accessible repositories. Implementing multi-factor authentication can also help reduce the risk of an LLMjacking attack. Through these measures, companies can significantly improve their security posture and better prepare themselves against such attacks.
Google's warning comes at a time when the use of large language models in the business world is increasing. Companies are increasingly relying on AI-powered solutions to enhance their efficiency and develop innovative products. However, this development also brings new challenges, particularly regarding security and the protection of sensitive data.
The threat of LLMjacking is an example of how cybercrime adapts to new technologies. Companies must remain vigilant and take proactive measures to protect themselves from such attacks. The costs that can arise from LLMjacking highlight the necessity of continuously updating and improving security strategies.
Ähnliche Artikel
Barracuda warns of critical security vulnerabilities
Barracuda Networks has warned of two critical vulnerabilities that could allow attackers root access to devices....
Cyberattack on Cooling Systems in European Supermarkets
A cyberattack has disrupted cooling systems in supermarkets across Europe, leading to significant issues....
Chinese hackers use ARTEX AI for attacks
Chinese hackers have used the ARTEX AI framework for automated attacks on over 200 organizations in 14 countries....
Greece introduces social media ban for children
Greece plans a social media ban for those under 15, placing responsibility on parents and platforms....
comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen