
Phishing campaign steals Google sessions
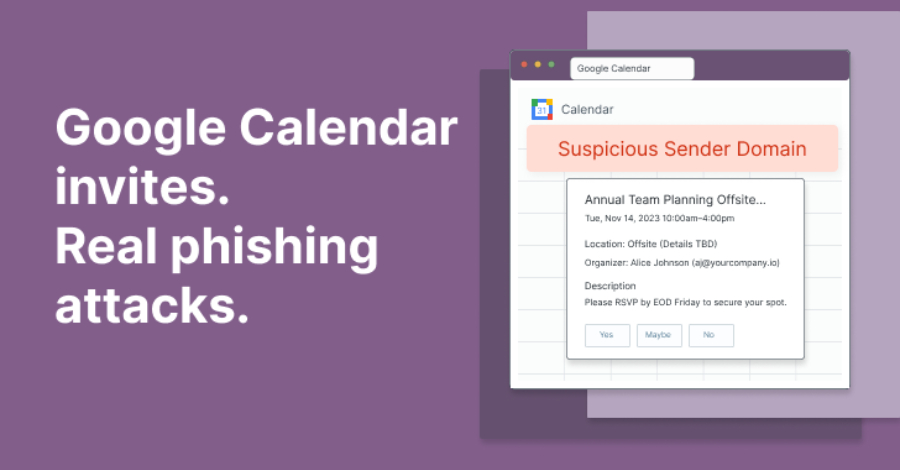
A new phishing campaign targets Google sessions of corporate users. Operation CloudFire has already removed hundreds of attacker domains.
Since mid-August 2026, a phishing operation targeting Google sessions of corporate users has caused significant damage. The threat was discovered by the Threat Research Team at Material Security, which describes the campaign as particularly sophisticated. The attackers have managed to craft their links in such a way that they are classified as safe during conventional security checks. This has allowed them to infiltrate user accounts unnoticed.
The campaign employs a variety of techniques to bypass user authentication. These include fake calendar invitations and live proxies that enable the attackers to impersonate legitimate users. These methods have outsmarted the security measures of many companies that rely on automated systems to detect phishing attempts.
Operation CloudFire
As part of their response to the threat, the team at Material Security has launched an initiative called Operation CloudFire. This operation aims to identify and neutralize the attackers' infrastructure. So far, hundreds of domains associated with the campaign have been successfully shut down. This measure is intended to prevent further users from becoming victims of the phishing attacks.
The attackers have specialized in exploiting weaknesses in Google's security protocols. By creating links that appear safe during a check, they can divert users' attention. This has led to an alarming increase in incidents where corporate data has been compromised.
Material Security has also emphasized that the attackers are not only targeting large companies but are also focusing on smaller firms and individuals. The flexibility of the campaign allows the attackers to quickly adjust their tactics and find new targets. This poses a significant challenge for the cybersecurity community.
The discovery of this campaign has led to increased awareness of the dangers of phishing. Companies are encouraged to review their security protocols and ensure that their employees are informed about the latest threats. Training on recognizing phishing attempts is an important part of these efforts.
The ongoing investigations by Material Security show that the threat from phishing campaigns continues to exist and evolve. The attackers are using increasingly sophisticated methods to achieve their goals. This requires constant adjustment of companies' security strategies to ensure the protection of their data.
The campaign has already led to a variety of security incidents that have resulted in both financial and reputational damage for the affected companies. The swift response from Material Security and the shutdown of attacker domains are crucial steps in the fight against this threat.
Ähnliche Artikel
eMudhra revokes additional CA certificates after security incident
eMudhra has revoked eight additional CA certificates after a security incident related to the handling of private keys w...
Cybercrime: Fake AI Domains in Focus
Cybersecurity researchers warn of 186 fake AI domains that mislead users and spread malware....
France accuses Iran after cyberattacks
France blames Iran for cyberattacks on supermarket cooling systems. The foreign minister announces consequences....
Notion reports security incident at Fireworks AI
Notion has announced a security incident at Fireworks AI that led to the disclosure of chat transcripts....
comment Kommentare (0)
Noch keine Kommentare. Schreiben Sie den ersten!
Kommentar hinterlassen